Security Center

Ensuring Information Security for Every Meari User
We follow industry best practices to provide reliable products and responsive support.
Report Vulnerability
Security Advisories
The Meari Product Security Incident Response Team (MEARI PSIRT) is responsible for receiving, handling, and publicly disclosing security vulnerabilities related to Meari products and solutions. It serves as the sole channel for the company to disclose vulnerability information for its products and solutions. MEARI PSIRT has implemented a comprehensive vulnerability management process that complies with ISO27001, ISO27701, ISO27017, and ISO27018 standards and follows industry best practices to promptly address identified vulnerabilities.
Security Technology
AES Encryption Algorithm: How Does It Work?2024-04-30
The Advanced Encryption Standard (AES), also known as the Rijndael algorithm, is currently the leading symmetric encryption algorithm internationally. AES falls under the category of block cipher algorithms within symmetric encryption algorithms.

What is a Symmetric Encryption Algorithm?2024-03-20
In the modern phase of cryptography, the concept of key confidentiality was introduced, giving rise to a new encryption algorithm paradigm known as the symmetric encryption algorithm.
Report a Vulnerability
1. Vulnerability Submission
We encourage users, partners, suppliers, security agencies, and independent researchers to proactively report any security risks or vulnerabilities related to MEARI products and solutions to the Meari PSIRT via email. Click the "Submit Vulnerability" button or send vulnerability information to security@meari.com.cn.
2. Email Submission Details(To facilitate timely verification and pinpointing of the vulnerability, the email should include the following information)
1.Organization / Title and Contact Information.
2.Description of the Potential Security Risk / Vulnerability.
3.Technical Details (e.g., system configuration, identification method, vulnerability description/screenshots, sample captured images, proof of concept (POC), steps to reproduce the issue, etc).
4.Product Name, Model, and Software/Firmware Version of the Reported Security Risk/Vulnerability.
5.Possible Vulnerability Disclosure Plan.

How We Address Vulnerabilities
Meari PSIRT strictly controls the scope of vulnerability information, limiting access to only those directly involved in addressing the issue.
Additionally, all individuals with access to this information are required to maintain confidentiality regarding the vulnerability until it is publicly disclosed.
Meari PSIRT discloses security vulnerabilities in the following two forms:
1.SA (Security Advisory): Publishes information related to security vulnerabilities in Meari products and solutions, including but not limited to vulnerability descriptions and remediation measures.
2.SN (Security Notification): Addresses security topics related to Meari products and solutions, including but not limited to vulnerabilities and security incidents.
Meari PSIRT adopts the CVSSv3 standard, providing a base score and temporal score for each security vulnerability assessment. Customers may also create their own environmental scores based on their specific needs.
For details on the specific CVSSv3 standard, please visit this link: https://www.first.org/cvss/specification-document
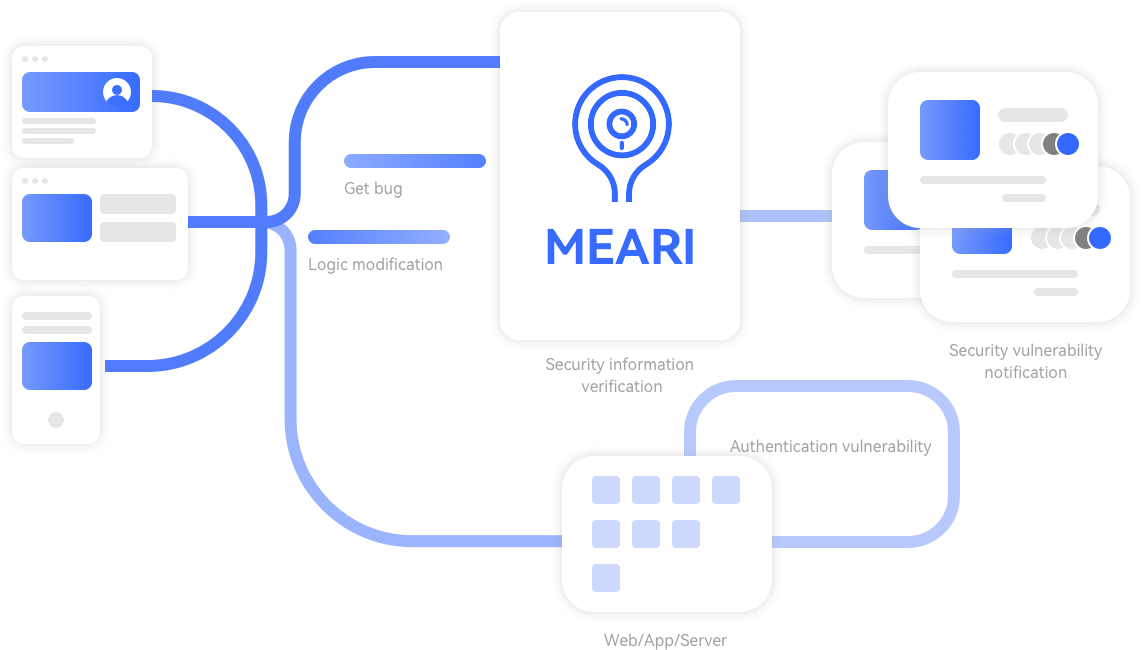
Our Vulnerability Handling Process
 1. ReceiptReceive and collect reports of suspected product security vulnerabilities. Acknowledge receipt within 2 business days and begin assessment.
 2. VerificationCoordinate with the relevant teams to verify the vulnerability and rate the risk. Address the issue and provide a conclusion within 7 business days of receiving the report. For complex issues, progress will be shared in a timely manner, and we will communicate with the reporter when necessary.
 3. RemediationThe business team drives remediation by severity and difficulty. Critical and high-risk vulnerabilities will be fixed, or a temporary mitigation deployed, within 24 hours where possible. Medium-risk issues within 3 business days, and low-risk issues within 7 business days. Some fixes depend on firmware or version release schedules; the actual timeline will be communicated promptly. Vulnerabilities with severe or major impact will have a separate emergency security advisory.
 4. DisclosureAfter a fix is available, we proactively disclose the vulnerability, release the fixed firmware or version, and update the public handling status. Vulnerabilities with severe or major impact will have a separate emergency security advisory. If coordinated or delayed disclosure is required, we will inform the reporter.
 5. ImprovementEnhance vulnerability scanning capabilities and integrate them into product security requirements